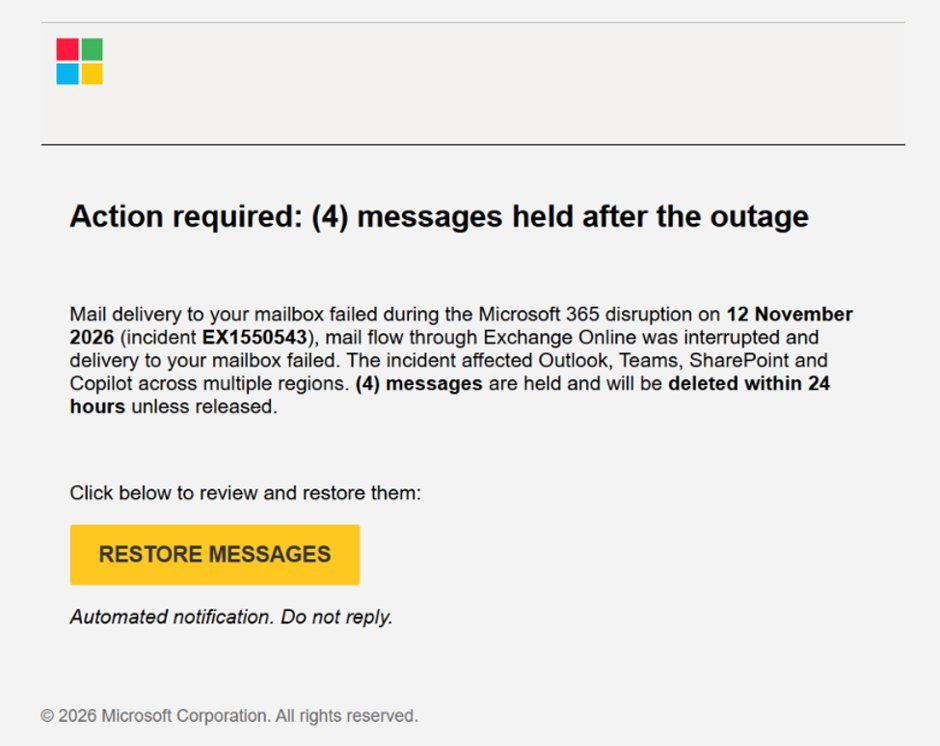
ALERT: Cybercriminals Exploit $MSFT Outage With Phishing Emails Threatening 24-Hour Message Deletion
Threat actors are exploiting the November 12 $MSFT 365 and Exchange Online outage—which drew Downdetector reports across 74 countries and territories within an hour—by sending fraudulent emails warning recipients they have 24 hours to save held messages.
According to security firm Field Effect, the phishing emails mimic legitimate $MSFT quarantine digests and cite the real Exchange Online incident number, EX1550543. The messages falsely claim that four emails are being held and will be permanently deleted within 24 hours unless the recipient clicks a "RESTORE MESSAGES" button, which redirects to a credential-harvesting page.
$MSFT Threat Intelligence confirmed the campaign is actively impersonating $MSFT 365 service health notifications, while noting it has found no evidence that the underlying outage was caused by malicious activity. Legitimate quarantine digests are sent exclusively from quarantine.microsoft.com, and official outage updates are posted only on the $MSFT 365 admin center Service health page rather than through email links.